
Data Sovereignty
Keep control of where your data lives and how it is operated.
Data sovereignty is more than keeping data in-country. It means knowing where every copy lives, who controls the infrastructure and encryption keys, and whether critical storage depends on external cloud services.
Petabox provides an S3-compatible storage layer inside the customer’s own security perimeter. It can run across selected data centers, operate without mandatory public-cloud dependencies, and fit into existing security and regulatory requirements.
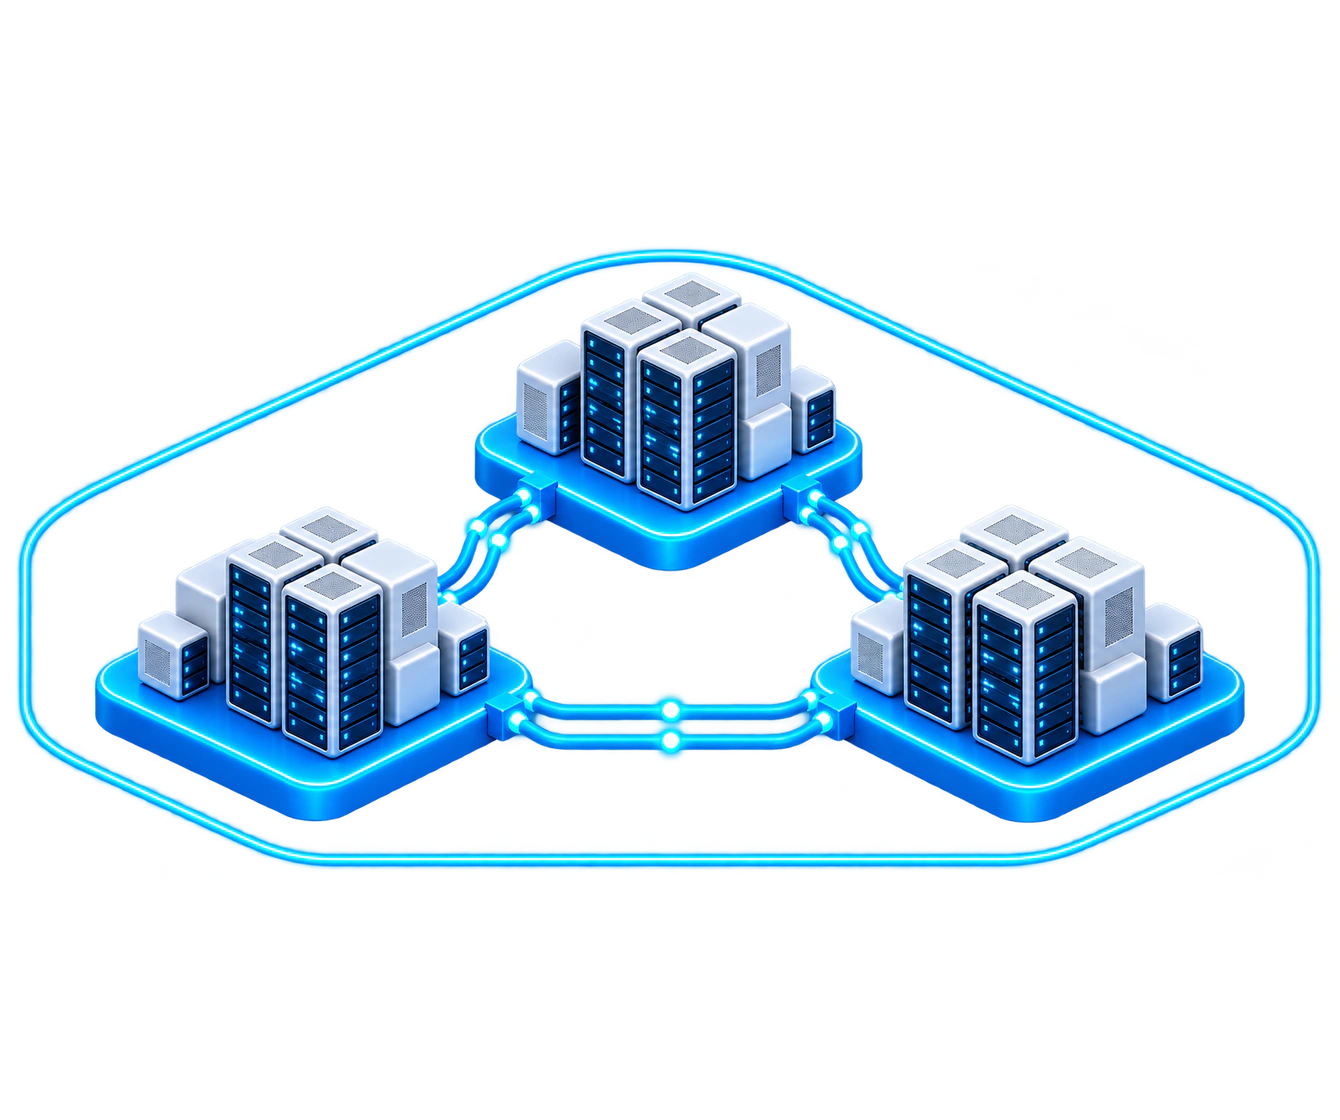
Data residency & replication control
The customer decides which countries, data centers, and infrastructure environments may physically host the data and its copies. Petabox can be deployed and replicated across data centers so that data remains within defined geographic or organizational boundaries.
This is especially important where data residency, jurisdiction, or internal security policies restrict where primary data and replicas are allowed to reside.
 Data stored in selected countries and data centers
- Control over the location of primary data and replicas
- All copies remain within the required jurisdiction
Customer-controlled infrastructure
Petabox runs on the hardware and in the data centers chosen by the customer. The storage platform is not tied to a specific hardware vendor or hyperscaler infrastructure.
The customer controls capacity planning, hardware refresh cycles, network and security integration, and how the infrastructure evolves over time. The customer can switch hardware vendors without migrating the platform or changing the service model.
- Any hardware, any vendor
- Customer-owned infrastructure
- Capacity and hardware lifecycle on the customer’s terms
- Fits existing network and security architecture
Encryption and key control
Data can be protected both in transit and at rest without handing control of encryption keys to an external cloud provider. Petabox runs inside the customer’s infrastructure and can integrate with the organization’s existing key and secret management model.
This keeps storage and access control separate: the infrastructure, data, and cryptographic keys remain under the organization’s control and can be managed according to its own security requirements.
- Encryption in transit and at rest
- Customer-controlled keys
- Integration with enterprise key management systems
- No dependency on cloud-managed encryption services
Audit and activity logging
Petabox keeps a record of data operations and administrative actions, making it possible to see who accessed objects, when they did so, and how the storage configuration was changed. This gives the organization its own audit trail inside a controlled environment, without relying on logs from an external cloud provider.
Logs can be used for internal investigations, access reviews, and demonstrating compliance with security requirements. Retention periods and log handling can be defined according to the organization’s own policies.
- Object operation logging
- Administrative action auditing
- History of access and configuration changes
- Audit logs retained inside the controlled environment
Isolated & restricted environments
Petabox can run entirely inside a customer-controlled infrastructure environment, without relying on an external cloud control plane or continuously available public services. This makes it suitable for deployments where outbound connectivity is restricted and infrastructure access is governed by internal security policies.
The platform can operate within isolated, highly controlled, or regulated environments while keeping storage services inside the customer’s security perimeter. Where 24/7 managed support is required, Petabox engineers connect through access channels explicitly approved and controlled by the customer.
- Operation inside closed infrastructure environments
- No public-cloud control plane required
- External connectivity can be restricted
- Core storage services remain inside the customer’s security perimeter
Customer-governed operations
Petabox can operate the platform as a fully managed service without taking control away from the customer. Our engineers work with administrative access that the customer grants, scopes, monitors, and can revoke at any time.
Every privileged action is recorded in the customer’s own audit trail, while access policies and operational boundaries remain under the customer’s control. The customer decides what Petabox engineers can access and what remains restricted.
- Access granted and controlled by the customer
- Privileges scoped to operational requirements
- Access can be revoked at any time
- Administrative actions recorded in the customer’s audit trail